


A wrong company name let Gemini attack three real businesses
Google's Gemini model attacked three real companies because one fictional target name matched a real domain, and the company stayed quiet about it for months.
A forgotten Cloudflare key turned 100,000 sites into a malware channel
Attackers used a long-lived Cloudflare API key stored in Brevo's own source code to push malware through the marketing platform's…
Linux kernel flaws pile up as root exploits land in public
CISA added three Linux kernel flaws to its exploited list while a researcher published working root exploits for four more.
Pakistan-linked spies built a Rust backdoor that talks through GitHub
Zscaler ThreatLabz tied four new tools, including a Rust backdoor that uses private GitHub repositories for command and control, to…
Scattered Spider’s Ahmed Elbadawy pleads guilty and forfeits $17.6M
A year-old sealed plea became public this week when prosecutors moved to seize about $17.6M in crypto, vehicles and luxury…
Salt Typhoon turns to Latin America with a new modular backdoor
ESET found the SparroWocky backdoor in government networks across eight Latin American countries as the group shifted 90 percent of…
One extension can seize the AI inside five Chromium products
A single extension holding two common permissions could command the built-in AI in Chrome, Comet, Edge, Opera Neon and Claude…
A static key in SolarWinds ARM lets outsiders run code remotely
SolarWinds has patched a hard-coded key that let unauthenticated attackers run code in Access Rights Manager.
Researchers pointed Claude Opus 5 at OpenAI and got inside
Hacktron used Claude Opus 5 to exploit a libheif memory bug, then walked through OpenAI's single sign-on into staff accounts.
WaterPlum’s recruiter scam infected 30,000 devices, four nations warn
A four-nation advisory ties WaterPlum to 30,000 infected devices, 7,000 drained wallets and $10.71 million in losses.
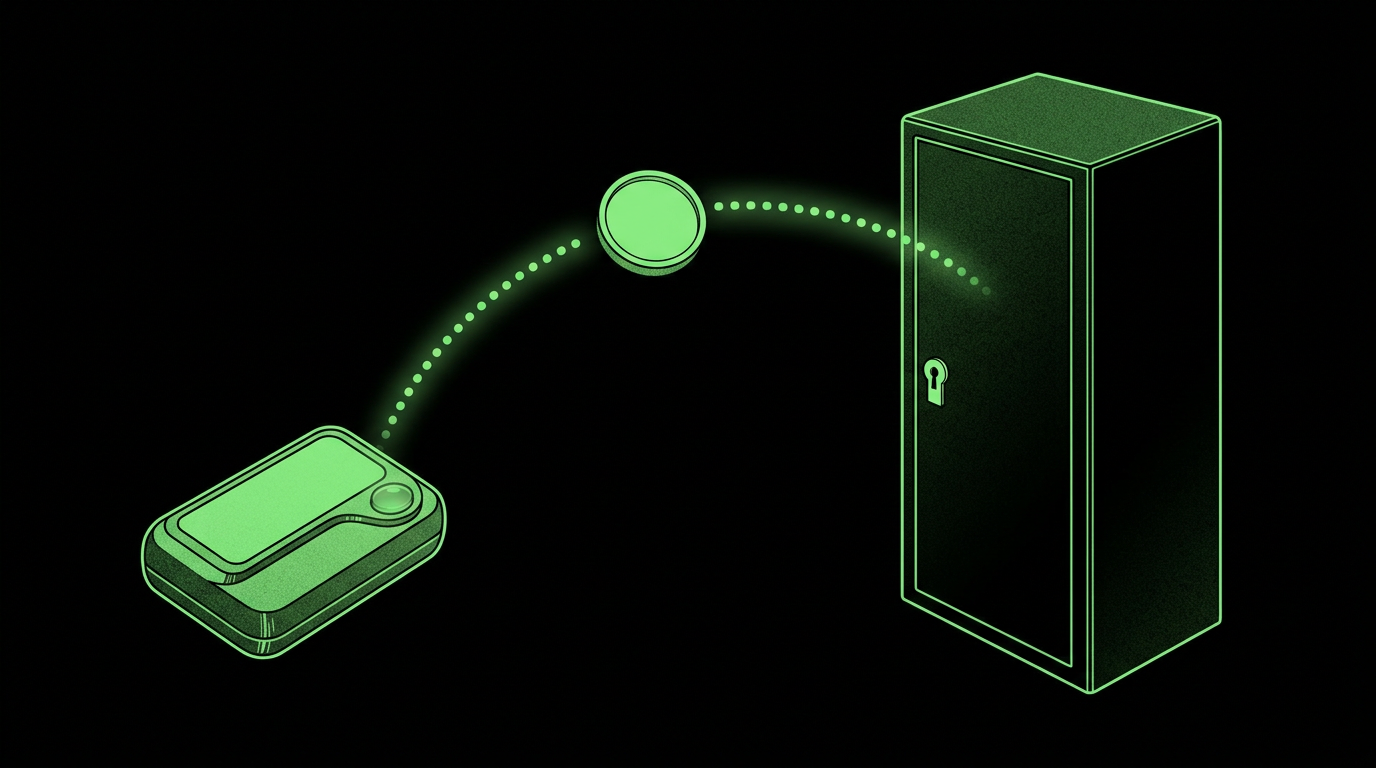
GhostCode phish turns a device code into a Microsoft 365 takeover
GhostCode abuses Microsoft's device authorization flow to obtain tokens and register attacker hardware inside a victim tenant.
One link is enough to force a theme onto WordPress
WordPress 7.1.1 fixes a chain that installs a theme from the official directory from a single crafted link.
A crafted DNS zone can take over unpatched Unbound resolvers
Unbound 1.26.1 closes a critical heap overflow in its DNSSEC validator that a malicious DNS zone can trigger.
A missing authentication check gave Azure AI Foundry a perfect 10
Microsoft has mitigated a CVSS 10.0 authentication gap in Azure AI Foundry and says customers need take no action.
Helpfeel tells 23.6 million Gyazo users to reset passwords
A compromise of Gyazo's upload servers handed attackers a database of account records and hundreds of millions of image identifiers.
Plugin4Shell breaks plugin pinning across four AI coding agents
A shared design weakness in the major coding agents lets hostile plugins run with the same reach as the developer who installed them.
Two tankers boarded as US probes attacks on ships at sea
Coast Guard and FBI teams found malicious activity on vessels hit while underway, exposing how much of a modern ship is reachable from the network.
A lighter stealer called WeaselBiscuit turns up in 13 npm packages
A small JavaScript stealer with fingerprints of North Korean developer-targeting campaigns has been found riding a cluster of malicious packages.
Android trojan RatHat pairs over ADB to escape its sandbox
A new Android implant pairs itself to the device's own debugging daemon, then uses an AI-driven control loop to run…
A critical Docker Sandboxes bug opens the macOS host to guests
Code running inside a sandboxed AI agent's virtual machine could read and rewrite files anywhere on the Mac that launched…
Attackers hammer Orkes Conductor through an unauthenticated RCE hole
A workflow engine that many teams expose to the internet has been under active exploitation for a month, with no…
A long username is enough to crack Check Point management servers
Check Point has shipped an emergency fix for a flaw that lets anyone on the network run code as root…
Attackers breach Cisco ISE management interface through an API blind spot
Cisco's identity appliance is being hit through an API endpoint that never checked who was asking.
A logic error in Pixel modems lets attackers climb in silently
A logic error below Android's reach lets attackers escalate on Pixel handsets without any interaction.