

Tag: Android
Android work profiles become a hiding place for Gigabud trojan
Group-IB found the long-running banking trojan building a second app that shelters inside Android's employer workspace.
Android Early Access window hides thousands of shady apps
Bitdefender says Google Play's Early Access program shelters thousands of deceptive apps.
StreamRat trojan rides fake TV apps to take over Android devices
ThreatFabric details StreamRat, an Android trojan pushed through fake TV streaming ads that can seize device control.
Android 17 blocks carrier snooping on visited websites
OS-wide Encrypted Client Hello in Android 17 hides visited domains from carriers and Wi-Fi snoops.
First malware rides legitimate car head unit updates
Kaspersky finds a downloader pushed through built-in firmware updaters of Android dashboards, tied to the MoYu Group.
Kimwolf botnet evolves to mimic browsers with HTTP/2 flood attacks
Unit 42 documents Kimwolf v7, a rebuild that hides DDoS floods behind browser fingerprints and Ethereum domains.
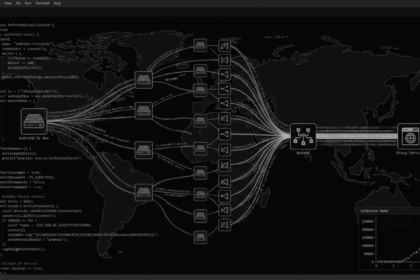
Popa botnet linked to NetNut residential proxy service infects millions of Android TV boxes
FBI identifies Popa Android botnet infecting millions of TV boxes through NetNut residential proxy service

Free Android VPN Apps Fail Basic Security Tests in Major Academic Study
A new automated testing framework reveals widespread traffic leaks, plaintext data transmission, and tracking behavior across 281 popular free Android…