A researcher has published two chained OnePlus flaws that together let an ordinary installed app take full root control of an Android phone, saying the vendor fixed neither before he went public. Rasmus Moorats demonstrated the attack on a OnePlus 15 running current OxygenOS, with no special permissions and no prompt shown to the owner.
OnePlus confirmed both issues in May and said they also affect many more OnePlus devices and phones from its sister brand OPPO, though it did not list which models. In the same reply the company asserted “the exclusive final right of vulnerability disclosure” and warned that publishing without consent could carry legal liability. Moorats released his findings on September 24.
Two bugs, one path to the kernel
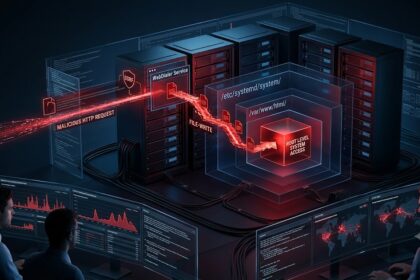
The first flaw sits in AtlasService, a debugging service that runs as root and accepts calls from any app without checking the caller. A crafted call feeds app-supplied text into a system command, granting root inside a restricted dumpstate zone. The second, in a hardware helper called olc2, runs any shell instruction it is handed, guarded only by a check that the caller is already root, which is exactly what the first bug provides. That step carries full low-level Linux privileges, including the ability to load kernel code.
The attack is local, so the app must already be on the device. There is no evidence it has been used in the wild, but with no patch available the risk sits with anyone running an affected handset.