
By using this site, you agree to the Privacy Policy and Terms of Use.
Accept
Threatwire
Search
  • Home
  • News & Alerts
  • Articles
  • Features
  • Spotlight
  • About
    • Mission
    • Services
    • Contact
  • Newsletter
  • Shop
    • All Items
    • By Category
      • Drinkware
      • T-Shirts
    • Cart
Reading: GhostCode phish turns a device code into a Microsoft 365 takeover
0

No products in the cart.

  • AI
  • Android
  • Authentication
  • Breaches
  • CASB
  • Compliance
  • Cryptography
  • Cyberinsurance
  • EDR
  • IAM
  • Malware
  • Phishing
  • Quantum
  • Ransomware
  • SecOps
  • SIEM
  • SOC
  • Threat Intelligence
  • Vulnerabilities
  • Zero Trust
ThreatwireThreatwire
Font ResizerAa
  • Home
  • News & Alerts
  • Articles
  • Features
  • Spotlight
  • About
  • Newsletter
  • Shop
Search
  • Home
  • News & Alerts
  • Articles
  • Features
  • Spotlight
  • About
    • Mission
    • Services
    • Contact
  • Newsletter
  • Shop
    • All Items
    • By Category
    • Cart
Follow US
  • About Threatwire
  • Services
  • Contact
  • Privacy
  • Legal
©2026 CybersecurityBeat. All Rights Reserved.
GhostCode phish turns a device code into a Microsoft 365 takeover
News & Alerts

GhostCode phish turns a device code into a Microsoft 365 takeover

GhostCode abuses Microsoft's device authorization flow to obtain tokens and register attacker hardware inside a victim tenant.

CSBadmin
Last updated: September 20, 2026 2:14 am
CSBadmin
2 Min Read
Share
SHARE

GhostCode is a phishing kit in which nothing the victim does looks wrong. The password is real, the multifactor prompt is real, and the sign-in completes exactly as Microsoft intends. Only the approval lands somewhere else.

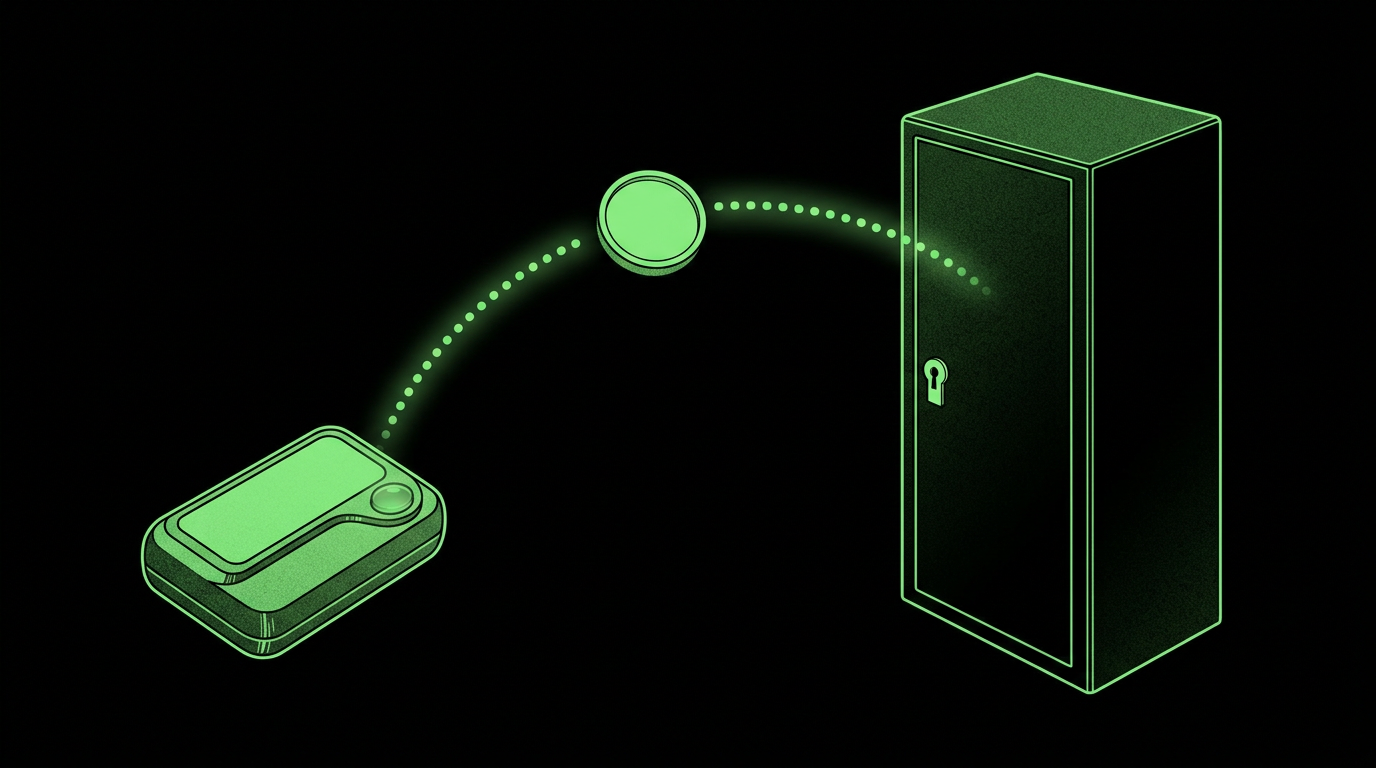
The kit turned up in the wild in late August 2026. Credit for spotting it goes to eSentire’s threat response unit. GhostCode rides on the OAuth 2.0 device authorization grant, a flow built for hardware that cannot render a browser sign-in: a smart TV or printer shows a short code, and the owner types it into a Microsoft page to finish authenticating. The kit asks Microsoft to mint its own code, hands it to the target, and waits for the sign-in to complete. The tokens that come out belong to the attacker’s device.

Persistence in under two minutes

What happens after the login sets this kit apart. eSentire’s logs captured nine successful API calls inside 78 seconds. By the time that burst ended, the operator’s tooling had already touched Microsoft Intune Enrollment, the Device Registration Service, Azure Active Directory and Microsoft Graph. Registrations followed at the 28, 53 and 77-second marks after sign-in. Three devices went in, and eSentire reads that spacing as machine-driven, not manual.

With that foothold, the operators enrol hardware of their own, harvest further credentials and hold ground a password reset alone may not clear.

The lure is deliberately dull. Attackers open with a procurement enquiry sent through a website contact form, move the conversation to an NDA-themed HTML file, and that file drops the victim on the device-code page.

The practical asks are to alert on unexpected device registrations and Intune enrolments instead of dismissing them as inventory noise, and to restrict the device-code grant through Conditional Access wherever the business can live without it.
CSBadmin

The latest in cybersecurity news and updates.

TAGGED:Account Takeoverdevice code phishingeSentireIdentity SecurityMicrosoft 365OAuthPhishing
SOURCES:CSO Online
Share This Article
Facebook Print
ByCSBadmin
Follow:
The latest in cybersecurity news and updates.
Previous Article One link is enough to force a theme onto WordPress One link is enough to force a theme onto WordPress
Next Article Fake coding tests backdoored 30,000 devices for North Korea WaterPlum’s recruiter scam infected 30,000 devices, four nations warn

Trending

A wrong company name let Gemini attack three real businesses
September 21, 2026
A forgotten Cloudflare key turned 100,000 sites into a malware channel
September 21, 2026
Linux kernel flaws pile up as root exploits land in public
September 21, 2026
Pakistan-linked spies built a Rust backdoor that talks through GitHub
September 21, 2026
Scattered Spider's Ahmed Elbadawy pleads guilty and forfeits $17.6M
Scattered Spider’s Ahmed Elbadawy pleads guilty and forfeits $17.6M
September 21, 2026

Related Stories

CSBadmin

cPanel and WHM Emergency Patches Address Three Critical Flaws

An archive cabinet bursting open and spilling photographic film strips
CSBadmin

Helpfeel tells 23.6 million Gyazo users to reset passwords

CSBadmin

Rebrandable Android Spyware Sold as White Label Malware Service

CSBadmin

Stealthy Cyber Espionage Hits Medical Research Platform

logo-twfull
  • About Threatwire
  • Services
  • Contact
  • Privacy
  • Legal

© 2026 Threatwire / Cybersecurity Beat. All rights reserved.