

Search
Tag: Access Token
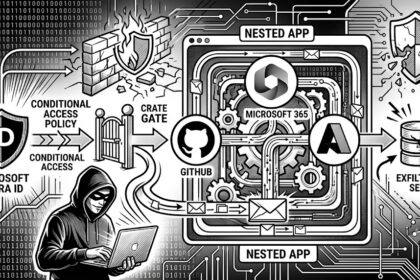
Conditional Access Bypass Exploits Microsoft Entra Nested App Flow
NetSPI researchers discovered that attackers can bypass Microsoft Entra Conditional Access Policies by abusing the Nested App Authentication OAuth flow…