

Search
Tag: C2
Ted implant rides trojanized HAProxy builds in South Korea
Rapid7 finds a North Korea-linked toolkit hiding inside trojanized HAProxy builds at two South Korean firms.
TWINLOOT hides inside Microsoft cloud to swipe logins and roam
New Windows implant TWINLOOT abuses SharePoint and Teams to steal credentials and move laterally.
Hollowgraph malware turns Microsoft 365 calendars into covert spy channels
Group-IB discovered HOLLOWGRAPH, malware that uses Microsoft 365 calendars as covert command channels with events dated to 2050.
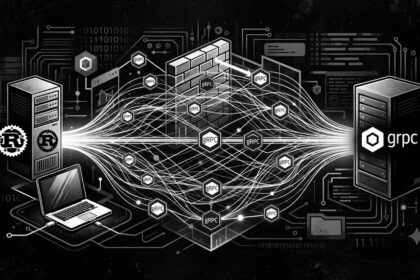
Rust Based MODBEACON Trojan Relies on gRPC Streaming for Stealthy C2
The memory resident Rust based trojan reuses the transport layer from an open source anti-censorship proxy framework to create encrypted…
Persistent Access Through Tailscale and OpenSSH Bypasses C2 Shutdown
A junior attacker used Tailscale and OpenSSH as a backup channel to maintain access to a compromised automotive business after…